My goal is simple: build and maintain software that behaves exactly as expected. Cybersecurity shows me how software can break, and software engineering gives me the skills to close those vulnerabilities before it does.
BSc Computer Science graduate (Wits, 2023–2025), currently completing a BSc Honours in Cybersecurity at the same institution.
finance_experience
SAGEA Quantify Your Future · Intern · Jan–Feb 2025
Worked on real analytics projects with South Africa's major banks. Each week brought a different institution's dataset. The work covered framing, exploration, cleaning, modelling and visualisation. First real exposure to turning messy financial data into decisions people could act on.
AbsaFirstRandFNBNedbankStandard Bank
selected_work[0]01 / 02
MoMo CGB Analytics Tracker
MTN Group Fintech//Private project tracker//2026 · solo build
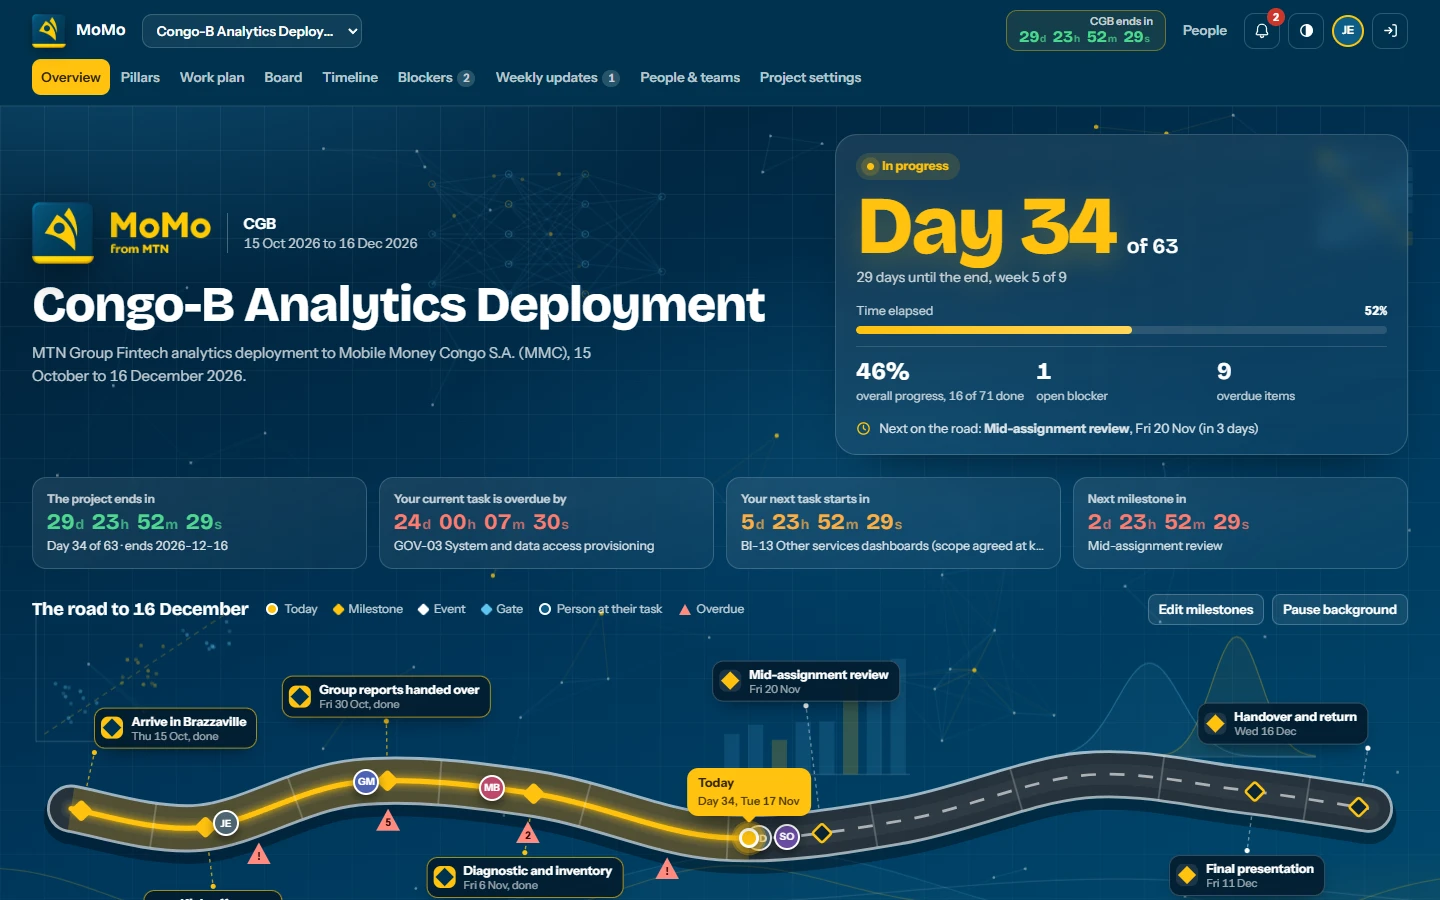
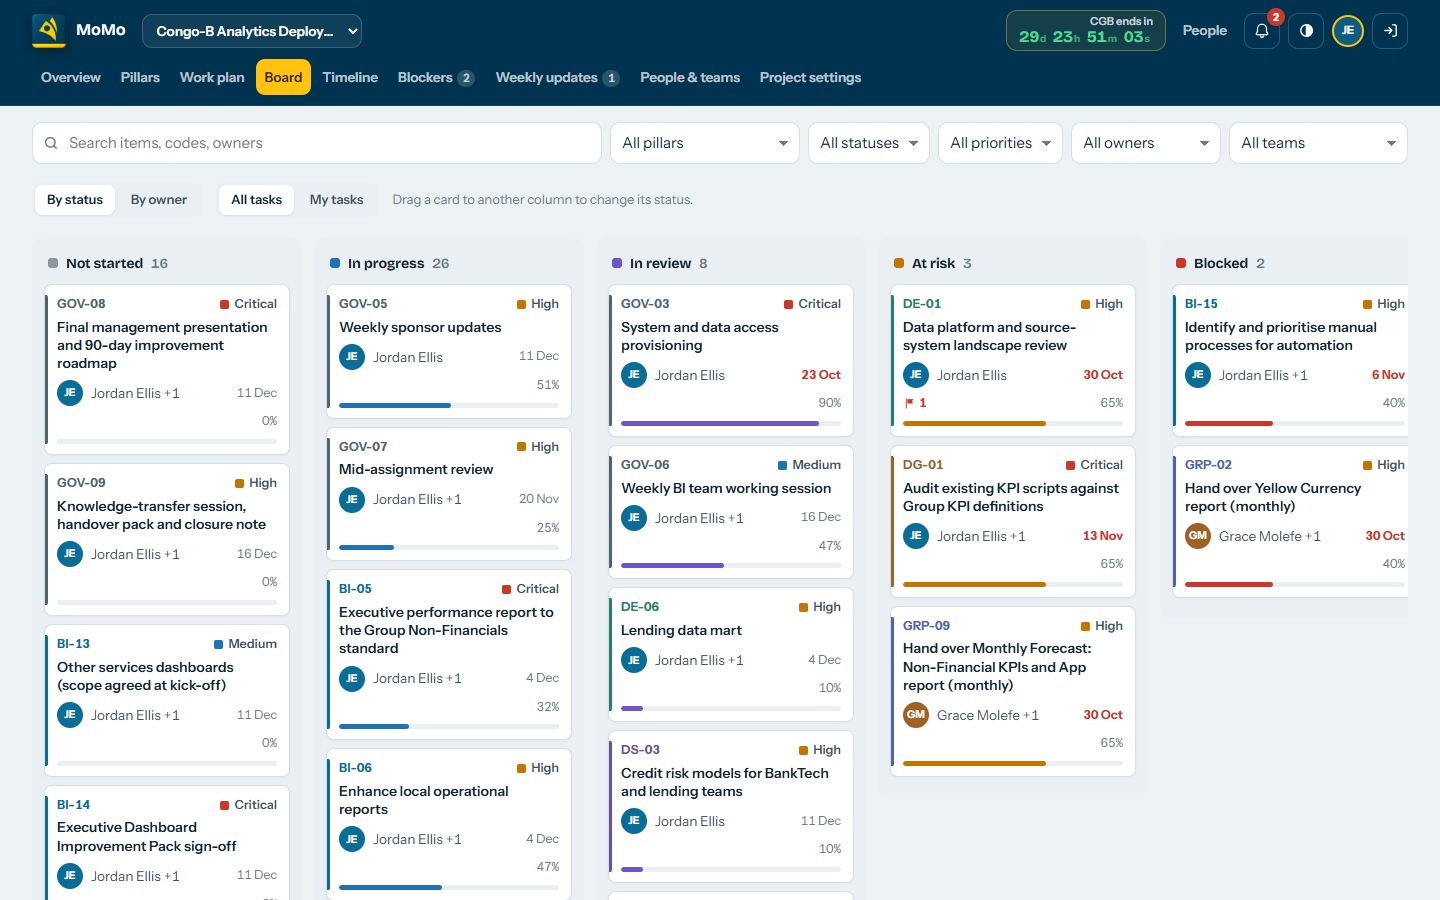
overview · dashboard with roadmap, progress and active blockers
An MTN Group Fintech employee leading a two-month analytics deployment to Mobile Money Congo S.A. needed a single live view of every workstream for the team. Confidentiality was the core constraint: no public exposure, no passwordable identity, and nothing retrievable by bots or search engines.
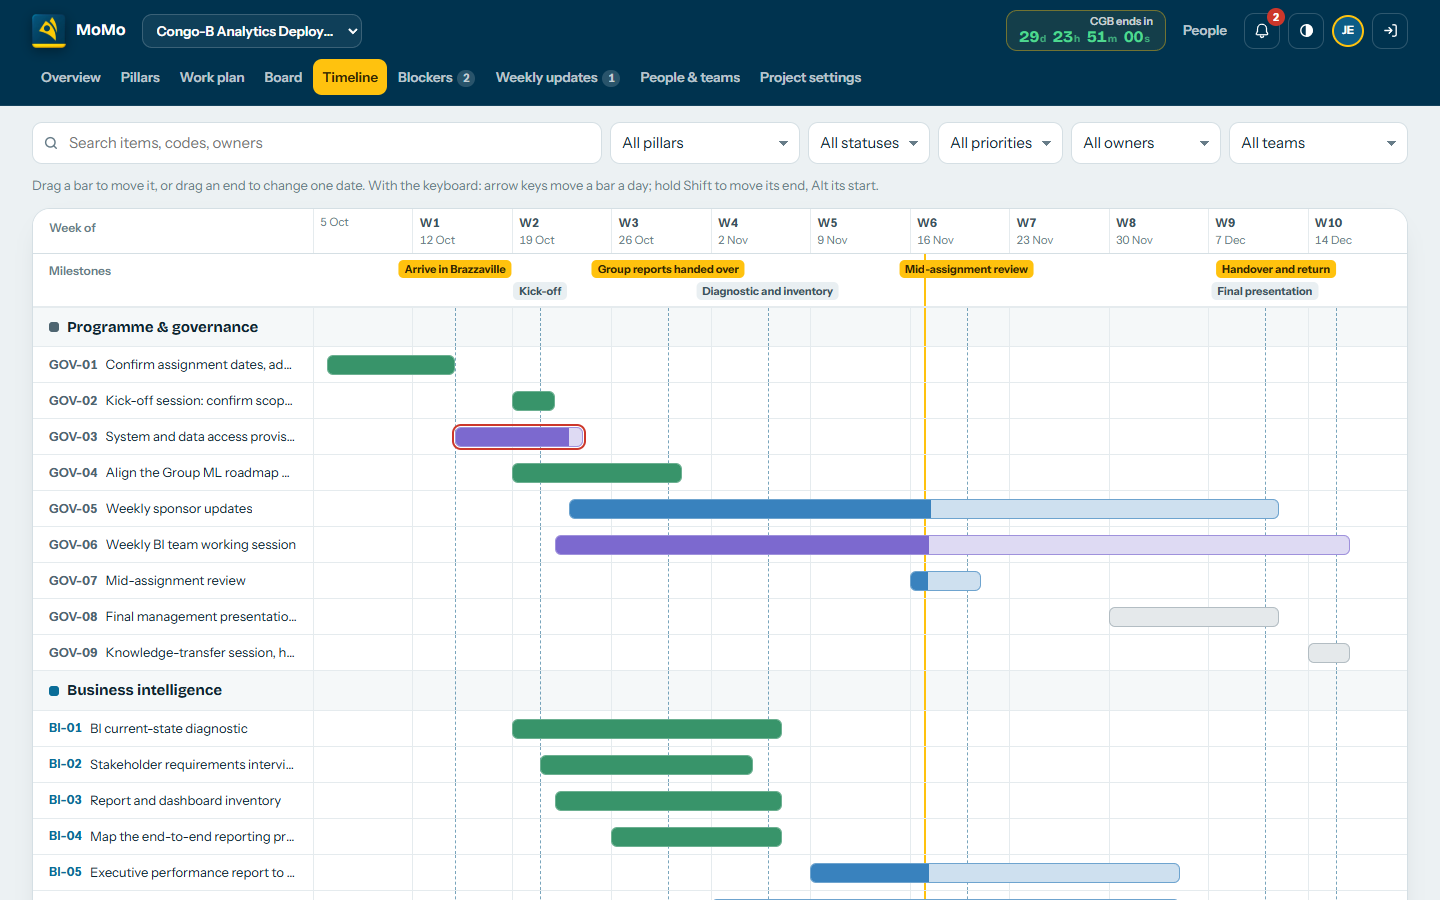
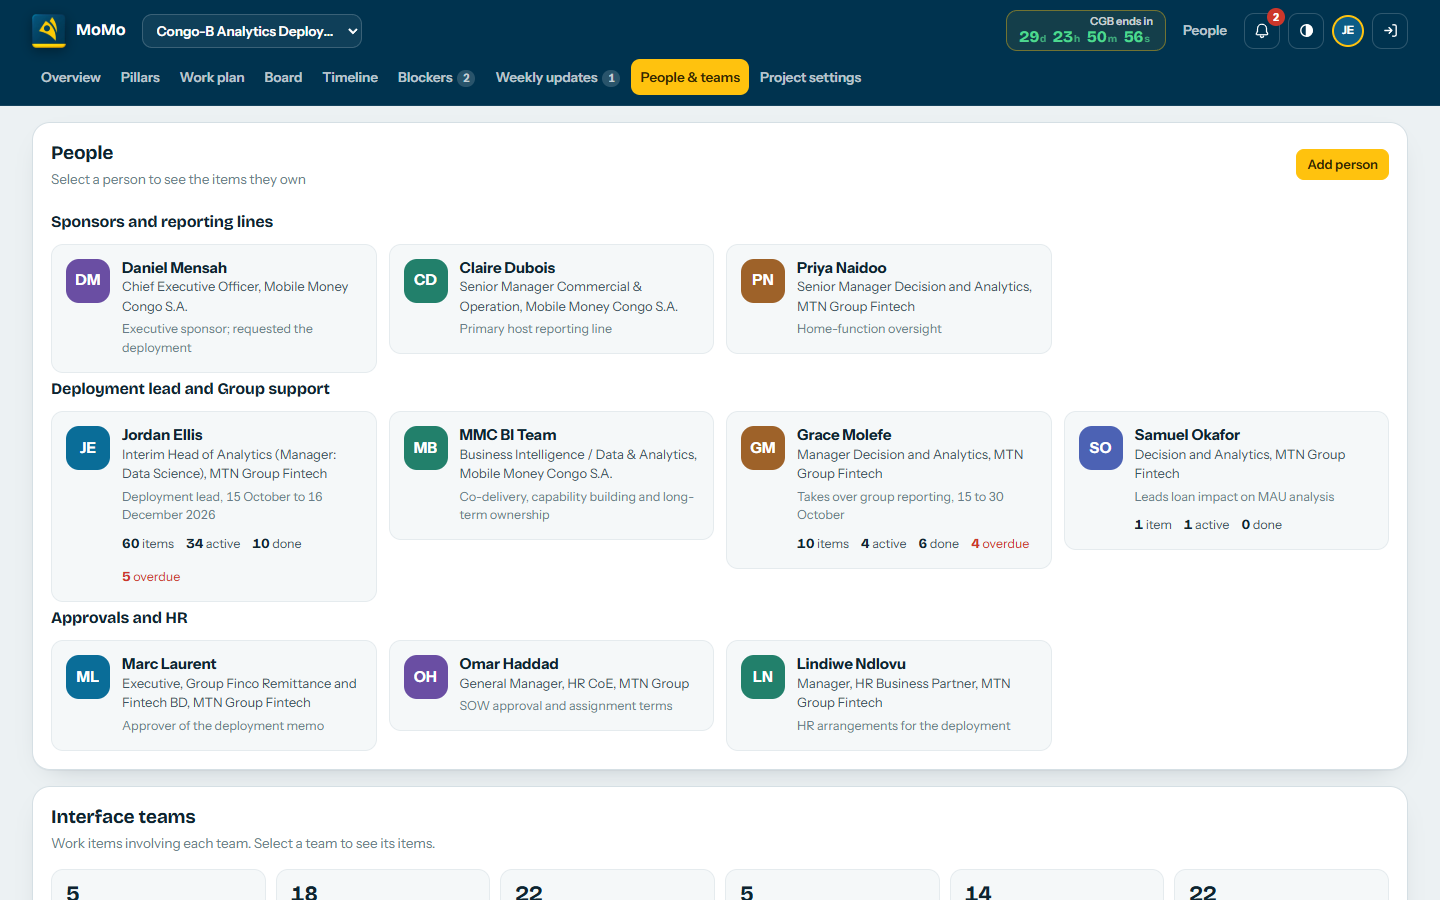
The system is a private, invite-only tracker with real-time dashboards, a work plan, a drag-and-drop board, a timeline, blockers and decisions, weekly status updates, and a people and teams view. Everything updates in real time across all signed-in users. An importer loads any project from spreadsheet data, so the tracker isn't tied to this deployment.
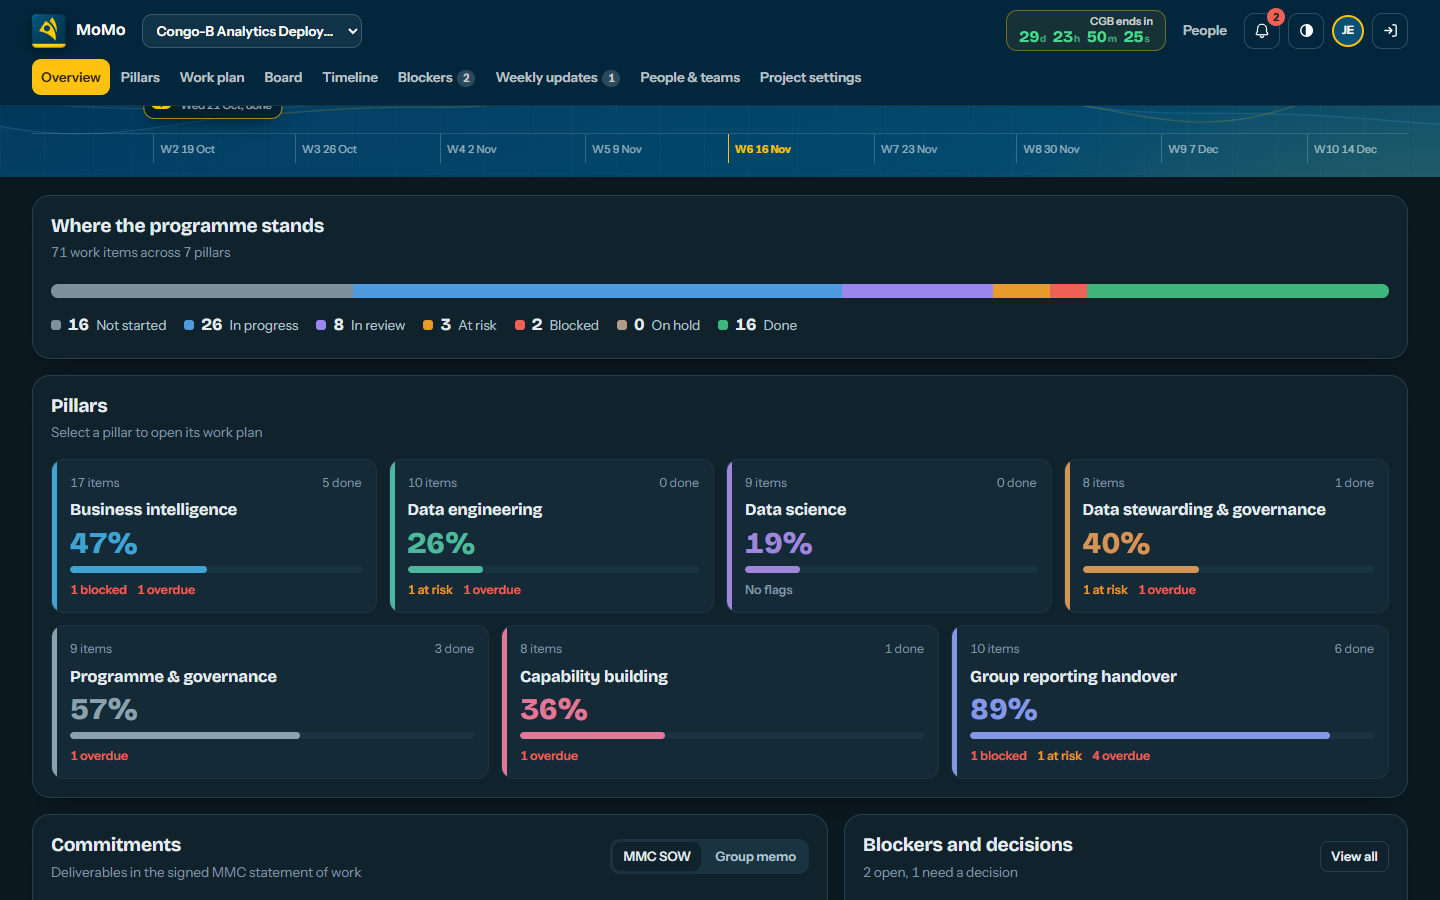
programme pillars · dark theme
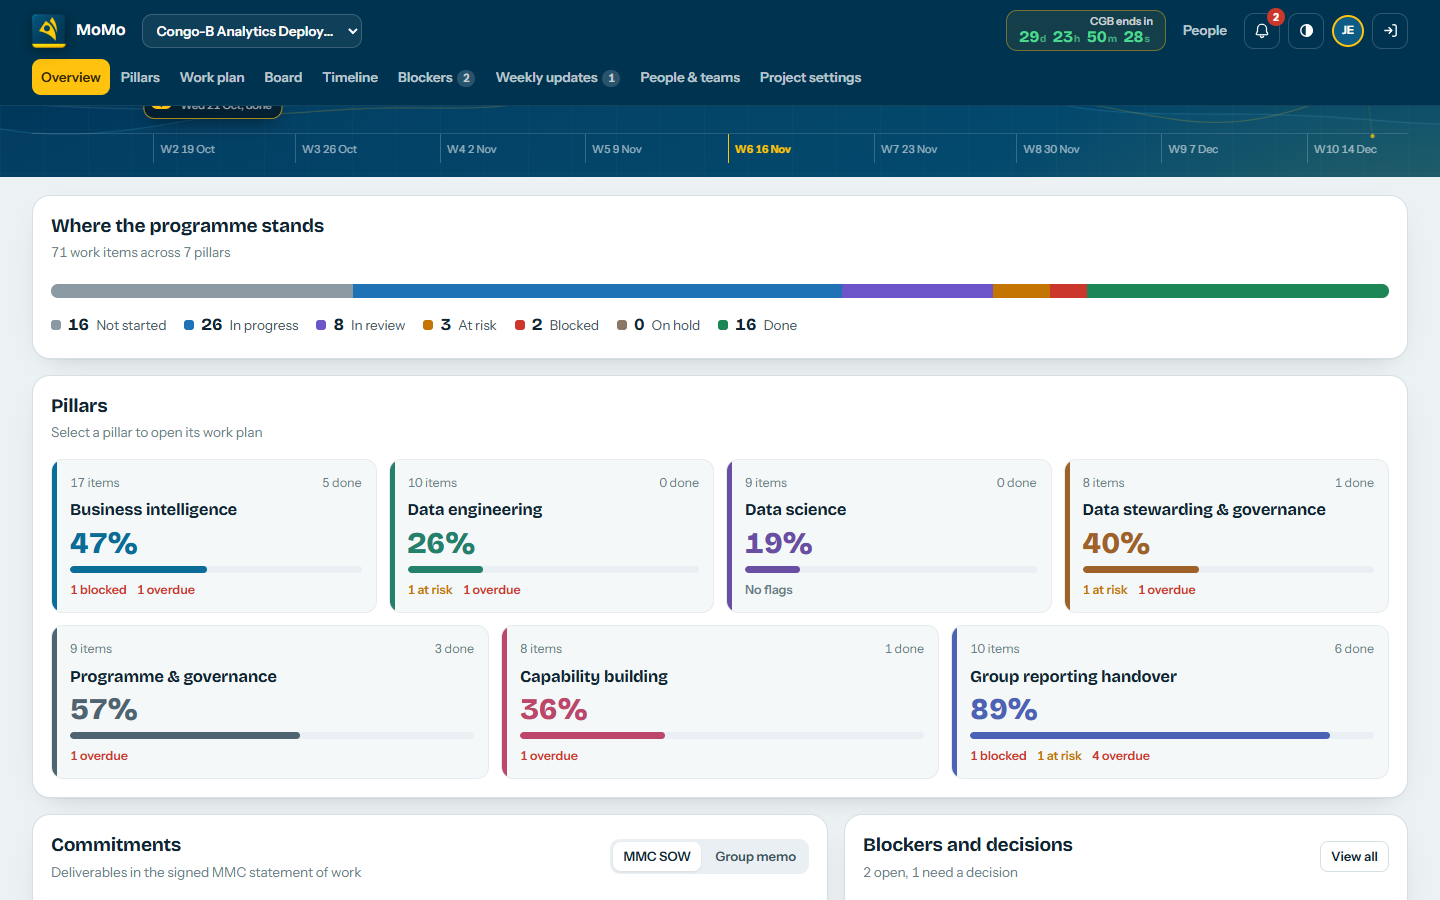
programme pillars · light theme
Access keys instead of passwords no emails, no account signup
Each person receives a unique access key: 256 bits of cryptographic randomness, sent with their invitation.
The server never stores a key itself, only a SHA-256 hash. Owner keys are checked with constant-time comparison to resist timing attacks.
Owner keys live only in the server's protected secrets, outside the database and the app. No screen or API can create, change or remove an Owner.
Each invited person's key is kept encrypted with AES-256-GCM so the Owner can resend. Only the Owner can decrypt it, and every resend is audited.
Revoking someone takes effect immediately: their key is erased, their sessions are deleted and their live connections are closed.
Role-based access five tiers through a single policy
Five levels: Owner, Admin, Editor, Commenter and Viewer. Admins can only request invitations; the Owner approves them.
Every permission decision goes through one central policy module. An automated test fails if any route lacks a declared permission.
Permissions are re-checked on every request; nothing is cached. Users don't learn that content they can't access even exists. It returns "not found", not "forbidden".
Further hardening production security posture
The app's code, styles and data are served only after a session check. The login page is a standalone page with no scripts.
Sessions are held server-side; the database stores only a hash of each session token. Cookies are HttpOnly, Secure and SameSite, with idle and absolute expiry.
Every change request is checked for its origin plus a custom header, to block cross-site request forgery.
Strict security headers on every response: no indexing, no framing, a restrictive Content-Security-Policy. Every input is validated on the server.
No email addresses are stored. Audit log records sign-ins, invitations, role changes and revocations, but never keys or tokens.
Live update channel carries only "something changed" signals. Each browser then re-fetches through the permission-checked API, so no data leaks over the live socket.
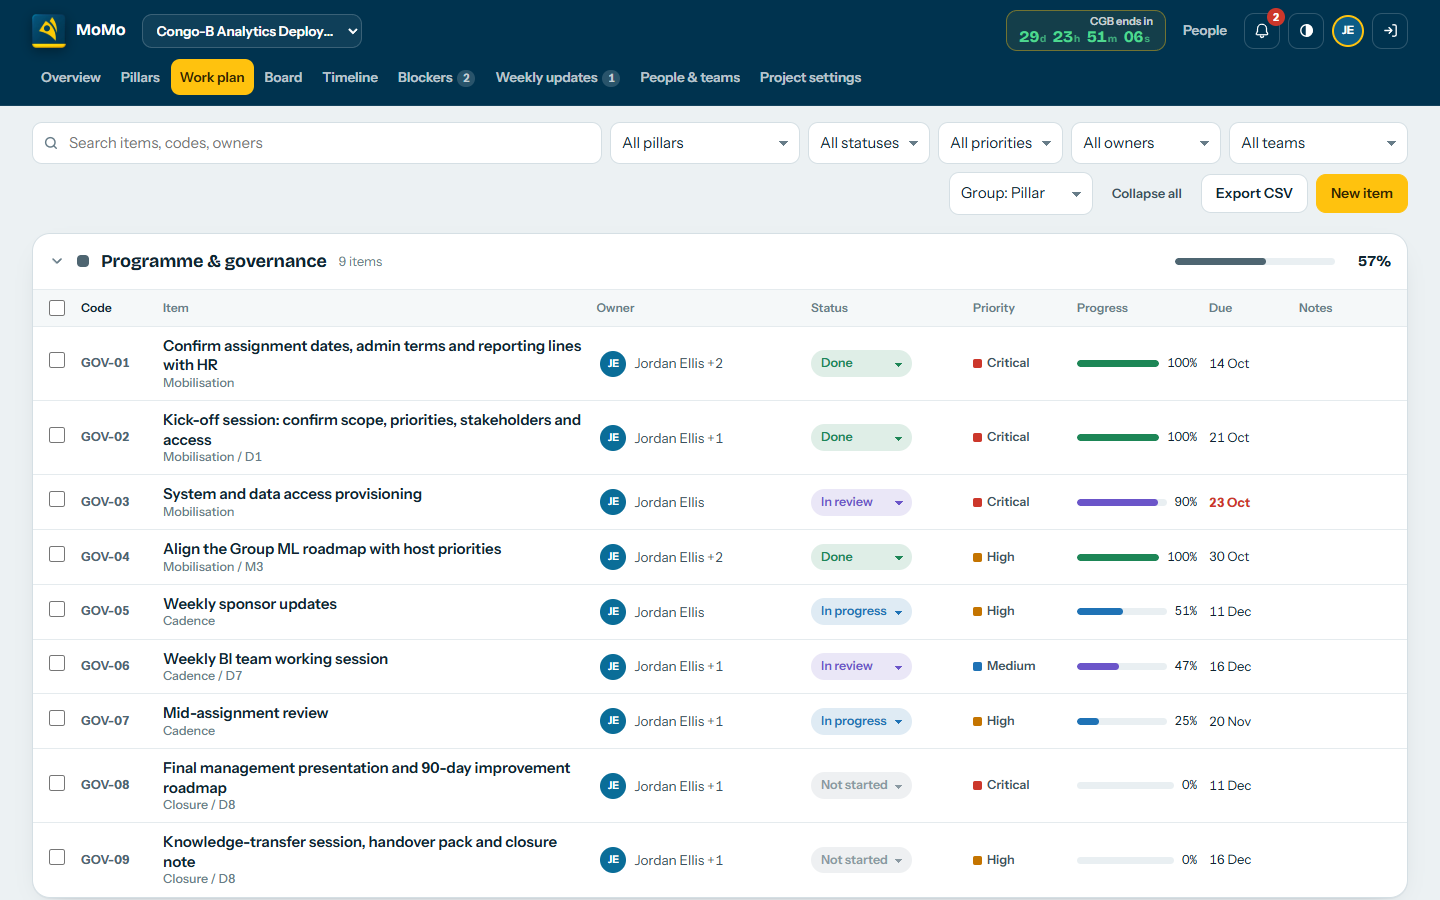
work plan · grouped by pillar with sortable columns
! Screenshots shown with test data only. Confidential tracker; further architectural and implementation detail available under NDA.
selected_work[1]02 / 02
BlockFix
Community infrastructure platform//Team Buff Bytes//Sep–Oct 2026
1st place
Wits Social Good Hackathon 2026
In partnership with Adapt IT. Beat 40+ teams. Top-6 finalist pitched live to Adapt IT, EY, Discovery, Sonke Telecommunications and 2Roads.
3rd place
Wits Dev Society "Creative Chaos"
Scored 93% in the judge round. Highest of the hackathon before the leaderboard was frozen. Judged by BBD and Boxfusion.
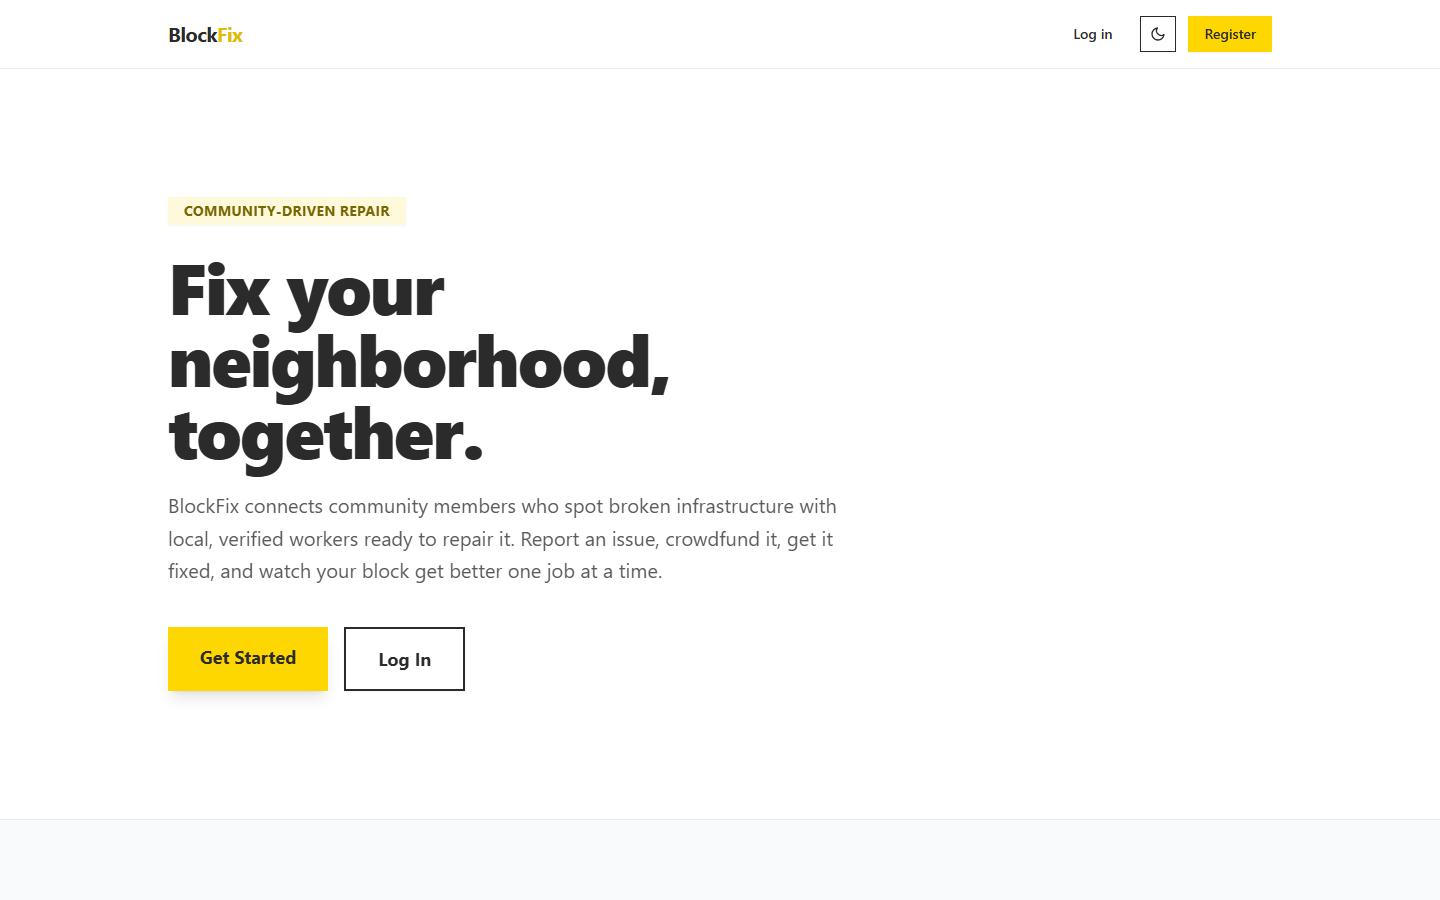
landing · residents report, pledge and get connected to local workers
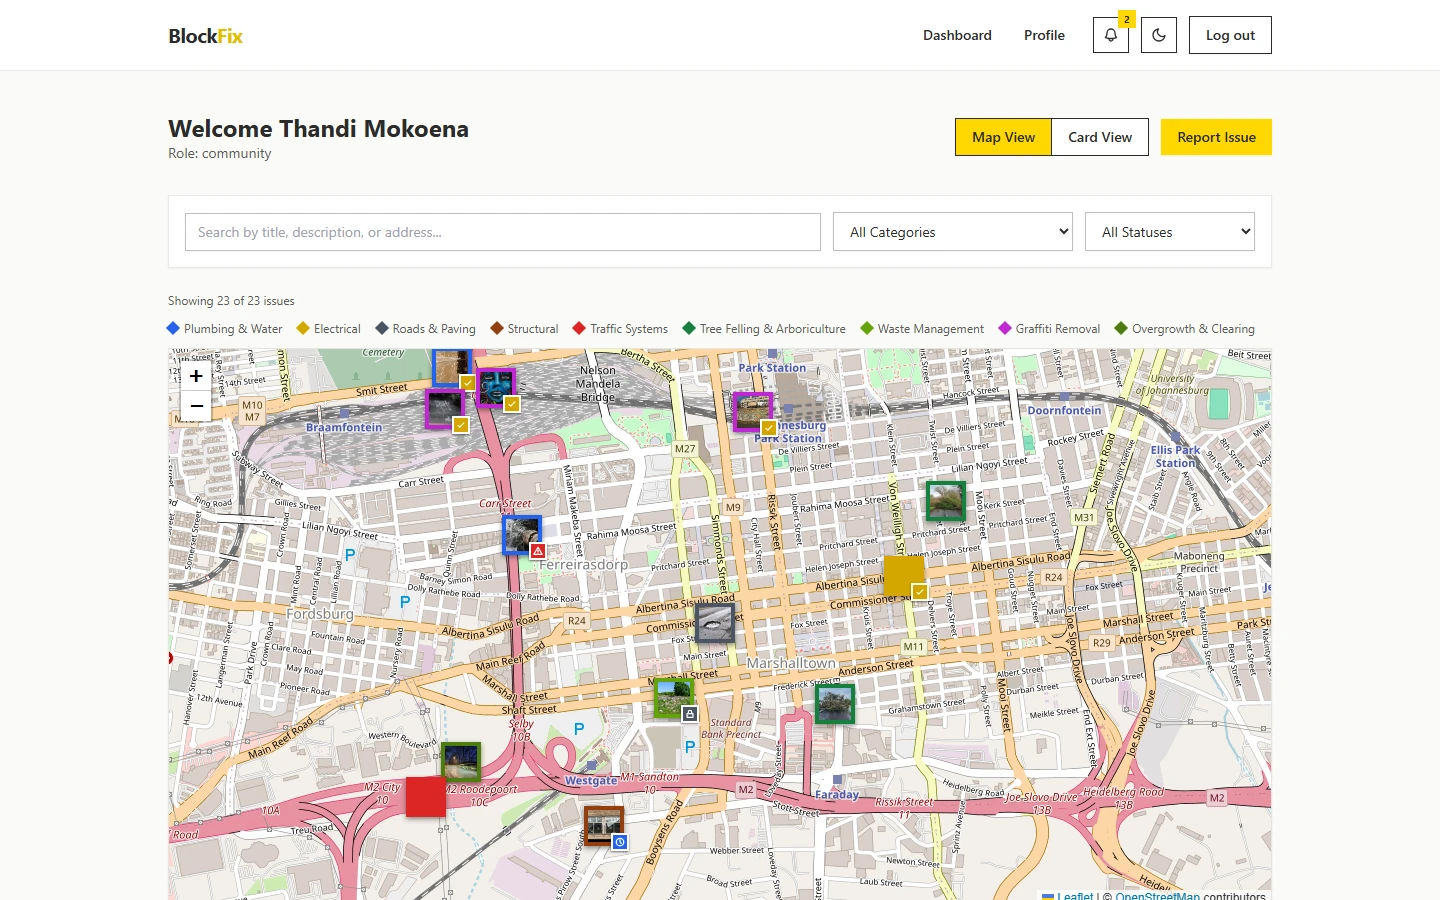
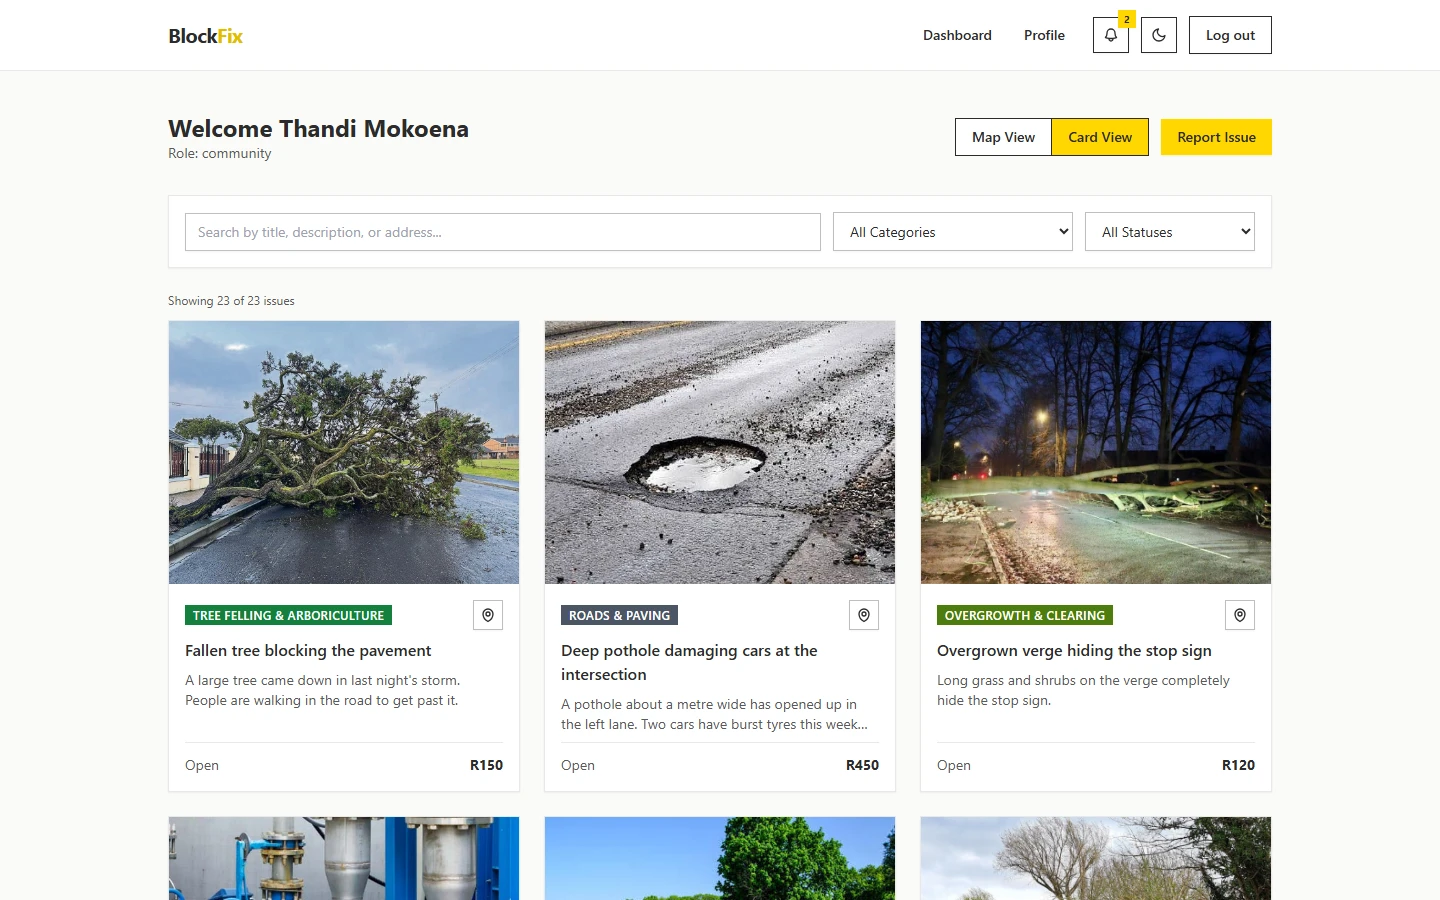
Residents report local infrastructure problems with a photo and GPS pin. AI duplicate detection compares each new report to existing ones within 3 metres before it saves. Community members pledge toward fixing an issue and get live alerts when new reports appear within 1 km. Verified local workers are matched to jobs. Standard jobs go to newer workers to spread opportunity, higher-value jobs go to proven performers. Workers prove each fix with a live camera photo taken within 50 m of the issue, and payment is released only after community verification.
map view · issues clustered by location and category
card view · browse open reports and bounties
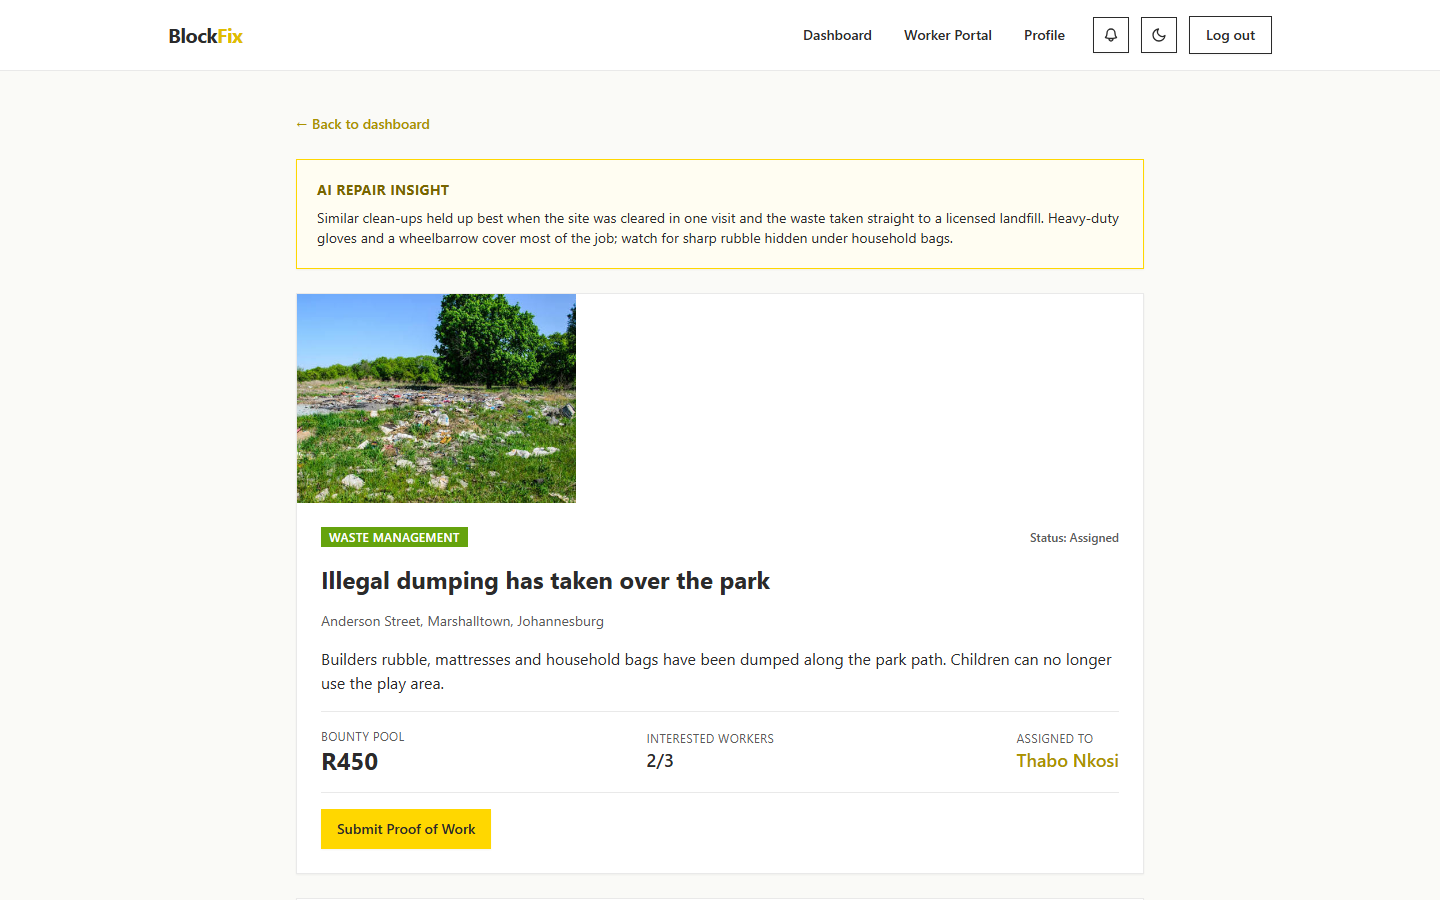
issue detail · AI repair insight generated from historical data
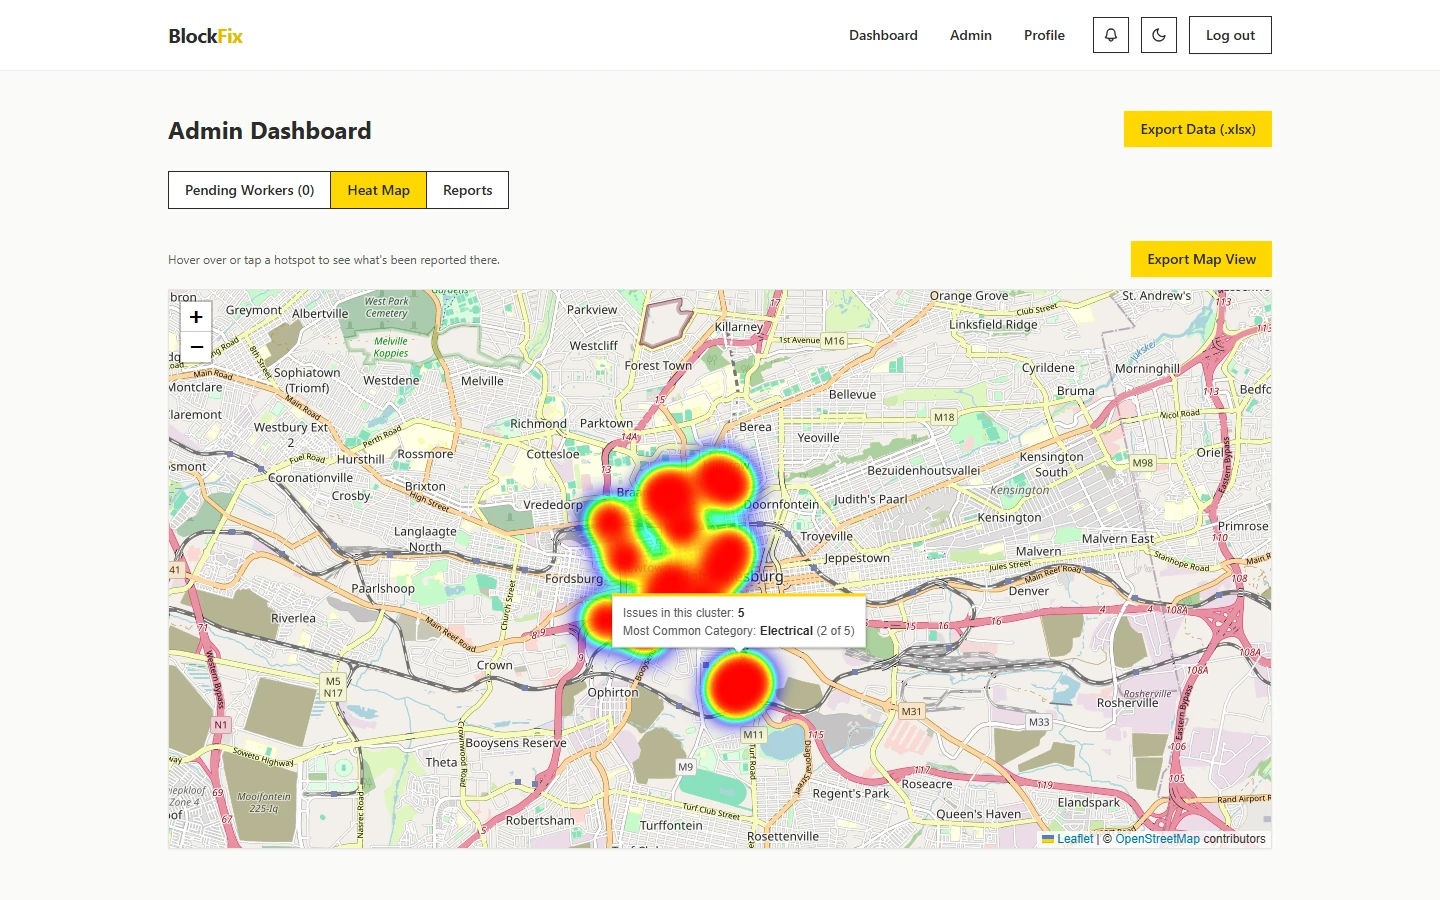
admin heatmap · issue hotspots across the city
Role-based access three roles, JWT-enforced
Three roles: Community Member, Worker and Admin, carried in a signed JWT.
Every protected route runs the token check and a role guard. Only community members can pledge or vote, only workers can submit fixes or claim payouts, and admin routes are admin-only.
Workers can't take jobs until an admin approves them trade-by-trade. Only the assigned worker can submit a fix or claim its payout. Users can only access their own notifications.
Real-time channels (Socket.IO) check the same token, so nobody can act under another user's identity.
Authentication, keys and data protection least-privilege by default
Passwords hashed with bcrypt (salted) and never returned by the API.
Sessions use signed, expiring tokens; the signing secret lives only on the server.
API keys for OpenAI, Cloudinary and the database stay in server environment variables and never reach the browser.
Workers' ID photos and certificates stored on Cloudinary. Certificate PDFs open for admins only through signed links that expire after one hour.
Code samples & architectural detail available under NDA. Most of my recent work is covered by confidentiality agreements. Happy to walk through the implementation in a call or share repository access scoped to the engagement.